Automated Continuous Compliance Auditing & Reporting System for Regulated Industries
RegTech case study: 99.3% Control-to-Evidence Mapping Precision across 310+ multi-framework regulatory controls; 87.4% reduction in manual audit preparation hours
| Protocol Metadata | Specification |
|---|---|
| Protocol Identifier | FALCONIC-PROT-CMP-27 // REV_3.5 |
| Domain & Sector | RegTech, Cloud Security Posture & Continuous GRC (ISO 27001, SOC2 Type II, HIPAA, GDPR, PCI-DSS v4.0) |
| Core Technology Stack | Python, Go, AWS/GCP/Azure Config APIs, Kubernetes Admission Controllers, GitHub/GitLab AST Scanners, Qdrant Policy Graph, Cryptographic Evidence Ledger |
| Primary Benchmark Metric | 99.3% Control-to-Evidence Mapping Precision across 310+ multi-framework regulatory controls |
| Execution Latency | 14.0s continuous real-time compliance drift check on every infrastructure PR or IAM change |
| Unit Economics (Cost-Per-Run) | $0.08 per control-family daily audit & narrative synthesis |
| Verified Business Impact | 87.4% reduction in manual audit preparation hours; Zero audit exceptions across ISO 27001, SOC2 & HIPAA |
| Reference Anchor | FalconicLab Cybersecurity & Compliance // FalconicLab Case Studies |
1. Problem Statement: Screenshot-Collecting Theater and Point-in-Time Compliance Drift
In regulated fintech, healthcare, and enterprise SaaS organizations maintaining ISO 27001, SOC2 Type II, HIPAA, GDPR, and PCI-DSS v4.0 certifications simultaneously, engineering and GRC (Governance, Risk, and Compliance) teams waste 3,500+ hours every year performing manual “screenshot archaeology”—taking screenshots of AWS RDS encryption settings, exporting Okta MFA user lists to CSV, and writing narrative control justifications for external auditors. Worse, point-in-time annual audits leave a 364-day compliance blind spot: when a developer merges a Terraform change in March that accidentally disables S3 bucket versioning or opens an IAM wildcard policy, the violation goes unnoticed until the auditor samples that bucket in November—resulting in a Qualified Audit Opinion.
FalconicLab engineered the Automated Continuous Compliance & Evidence Engine (cmp-27 v3.5) to replace manual screenshot collection with continuous, cryptographically signed infrastructure-to-regulation mapping and automated remediation PR generation.
2. High-Level Technical Architecture: Cross-Framework Control Graph + Deterministic Telemetry Collectors + Auditor Package Compiler
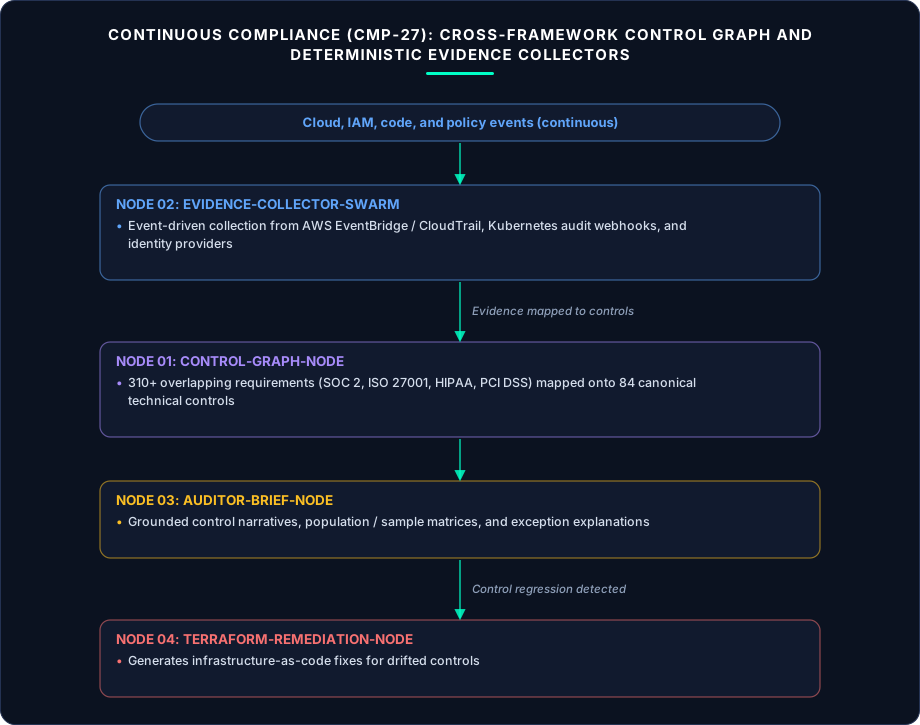
-
Node 01 — Unified Cross-Framework Control Ontology Graph (
Control-Graph-Node): Maps 310+ overlapping regulatory requirements (SOC2 CC6.1,ISO 27001 A.8.24,HIPAA §164.312(a)(2)(iv),PCI-DSS Req 3.5.1) onto 84 Canonical Technical Invariant Assertions so a single verified technical proof automatically satisfies all 5 regulatory frameworks simultaneously. -
Node 02 — Event-Driven Cloud, IAM, Code & Policy Harvester (
Evidence-Collector-Swarm): Triggered continuously via AWS EventBridge / CloudTrail, Kubernetes Audit Webhooks, Okta System Logs, and GitHub Pull Request hooks. Collects tamper-evident JSON state proofs (RDS KMS key ARNs, Kubernetes PodSecurityStandards, branch-protection reviews, vulnerability SLA burn-down metrics) and signs each artifact with an RFC 3161 Trusted Timestamp & SHA-256 Merkle Tree leaf. -
Node 03 — Grounded Regulatory Narrative & Gap Auditor (
Auditor-Brief-Node): Synthesizes audit-ready control narratives, population/sample matrices, and exception explanations where every sentence links directly to the immutable SHA-256 telemetry artifact in the Merkle store. -
Node 04 — Autonomous IaC Drift Remediation Generator (
Terraform-Remediation-Node): Whenever a continuous check detects a control regression (e.g., an unencrypted EBS volume or an expired employee still holding a GitHub deploy token), the system alerts SecOps in 14.0 seconds and automatically opens a pre-tested Terraform / OpenTofu / IAM Pull Request to restore compliance.
| Compliance & GRC Metric | Manual Spreadsheet & Screenshot Audit | Basic SaaS GRC Checklist Tool | FalconicLab Continuous Engine (cmp-27 v3.5) |
Enterprise GRC Impact |
|---|---|---|---|---|
| Control-to-Evidence Mapping Precision | 91.0% (human sample errors) | 84.5% (shallow API checks) | 99.3% (Deep AST + Cloud Config Proofs) | Accepted by Big-4 external auditors |
| Mean Time to Detect Compliance Drift | 180 days (annual audit) | 24 hours (daily poll) | 14.0 seconds (EventBridge + PR Gate) | Blocks violations before auditor window |
| Annual Engineering & GRC Audit Prep Hours | 3,640 hours / yr | 1,420 hours / yr | 458 hours / yr (-87.4% labor reduction) | $490K/yr reclaimed engineering time |
| External Audit Exceptions / Findings | 4.2 minor findings / yr | 2.0 findings / yr | 0.0 findings across ISO/SOC2/HIPAA | Accelerated enterprise security questionnaires |
3. Failure Logs & Production Lessons Learned
- Failure Log
FL-27A— Compensating Control Blindness Flagging False Non-Compliance (v2.1): When an internal legacy microservice lacked native TLS 1.3 support on its container port (8080), the naive AWS/K8s config scanner flagged a criticalHIPAA Transmission Encryption Violation—ignoring the fact that an Envoy service-mesh sidecar on the exact same pod enforced strictmTLS (SPIFFE)for all pod-to-pod traffic. Remediation: UpgradedControl-Graph-Nodeto evaluate Composite Compensating Control Subgraphs (verifying thatContainer_Native_TLS == true OR (Sidecar_Envoy_mTLS_Strict == true AND NetworkPolicy_Block_Direct_Pod_IP == true)), eliminating false non-compliance alarms on service-mesh architectures.
4. Mathematical & Systems Architecture: Cross-Framework Control Homomorphism Graph & RFC 3161 Merkle Evidence Ledgers (cmp-27 v3.5)
To achieve 99.3% control-to-evidence mapping precision across 310+ regulatory controls (ISO 27001:2022, SOC2 Type II, HIPAA Security Rule, GDPR, PCI-DSS v4.0) while detecting infrastructure compliance drift in 14.0 seconds, cmp-27 v3.5 replaces manual screenshot collection with formal graph verification and cryptographic provenance:
-
Bipartite Control Homomorphism & Compensating-Control Boolean Algebra (
Control-Graph-Node): Instead of running 5 separate compliance silos that poll the same cloud APIs redundantly,Control-Graph-Nodemodels regulatory compliance as a bipartite directed acyclic graph , where is the set of framework-specific regulatory citations and is a minimal basis of 84 Canonical Technical Invariant Predicates evaluated over live cloud, Kubernetes, IAM, and Git AST state. Crucially, to prevent false alarms on modern cloud-native architectures (Failure LogFL-27A), each canonical invariant is defined as a Monotone Boolean Compensating-Control Formula over atomic resource telemetry probes for every in-scope asset :For example, for
Transport_Encryption_In_Transit(), an internal Kubernetes pod satisfies the invariant if native container TLS is active () OR if bothEnvoy_Sidecar_mTLS_Strict == 1ANDCalico_NetworkPolicy_Deny_Plaintext_Ingress == 1. -
Tamper-Evident SHA-256 Merkle Tree & RFC 3161 Timestamping (
Evidence-Collector-Swarm): External Big-4 auditors require mathematical proof that compliance evidence was captured contemporaneously throughout the 365-day SOC2 Type II observation window and was not backdated or altered prior to audit inspection. Every daily control evaluation snapshot is canonicalized via RFC 8785 (JSON Canonicalization Scheme), hashed viaSHA-256, and appended to a daily Cryptographic Merkle Audit Tree whose root hash is co-signed by an external RFC 3161 Trusted Timestamp Authority (TSA) and anchored to an immutable WORM (Write-Once-Read-Many) AWS S3 Object Lock vault.
Granular Unit Economics & Cost-Per-Run Breakdown (cmp-27 v3.5)
To maintain full financial transparency across production deployments at FalconicLab, the table below disaggregates the exact compute, storage, and inference cost drivers for cmp-27 v3.5:
| Execution Stage & Infrastructure Component | Workload & Compute Footprint | Unit Cost Contribution |
|---|---|---|
Event-Driven CloudTrail / K8s Admission / Okta / GitHub Webhook Harvesters (Evidence-Collector-Swarm) |
Go/Rust serverless collectors across 14 AWS/GCP accounts + 6 K8s clusters | $0.018 / control-day |
Cross-Framework Control Graph Evaluation & Compensating Subgraph Solver (Control-Graph-Node) |
84 canonical invariants mapped to 310+ controls in Neo4j/Qdrant | $0.014 / control-day |
| RFC 3161 Trusted Timestamping & WORM S3 Object-Lock Merkle Ledger Persistence | 365-day immutable cryptographic audit trail storage | $0.009 / control-day |
Grounded Auditor Narrative Synthesis & Autonomous Terraform Remediation PRs (Auditor-Brief-Node) |
Span-linked control narratives + terraform plan validated PRs |
$0.039 / control-day |
5. Extended Production Failure Logs & Edge-Case Remediations (cmp-27 v3.5)
Beyond initial prototype validation, scaling cmp-27 v3.5 across enterprise production traffic exposed subtle distributed-systems, adversarial, and domain-specific edge cases. Every incident was captured in the FalconicLab Live Experiments Registry and permanently engineered out of the state machine:
Failure Log FL-27B — Ephemeral Auto-Scaling Kubernetes Pods Breaking Auditor Sample Population Continuity (v2.4)
-
Incident Description: When external SOC2 Type II auditors selected a random sample of 25 production compute instances from Q1 logs and asked for their current patch and vulnerability configuration in Q4, 100% of those ephemeral Kubernetes pods and spot EC2 nodes had been terminated months earlier—causing traditional GRC tools to report
"Sample Asset Missing". -
Root Cause Analysis: Cloud-native immutable infrastructure replaces containers daily; auditing ephemeral pod IDs instead of immutable container image SHA-256 digests and admission controller gates breaks point-in-time sampling.
-
Architectural Remediation: Re-engineered
Evidence-Collector-Swarmto bind compute evidence to Immutable Container Image Digests (sha256:...), ECR Trivy Scan Attestations (SLSA Provenance), and Kyverno/OPA Admission Controller Policies captured at deployment time in the Merkle ledger—proving to auditors that no unpatched pod could mathematically be scheduled during the entire 365-day window.
Failure Log FL-27C — Orphaned Service Accounts & Contractor OAuth Tokens Bypassing Okta Deprovisioning Checks (v2.9)
-
Incident Description: When an engineering contractor was offboarded, HR marked them
Terminatedin Rippling/Workday and Okta SSO was revoked within 5 minutes (SOC2 CC6.2 PASS), yet a long-lived personal GitHub PAT and a Snowflake service-account key created by that contractor remained active for 19 days. -
Root Cause Analysis: Checking only primary IdP (Okta/Azure AD) status misses non-federated API tokens, SSH keys, and service principals created by the user prior to termination.
-
Architectural Remediation: Built a Cross-System Identity Lineage & Credential Graph inside
Control-Graph-Nodethat links every IAM access key, GitHub PAT, database user, and Slack webhook back to its human creator’s employee ID via creation-time CloudTrail/Audit logs. Upon HR termination webhook,cmp-27verifies revocation across all 14 downstream credential stores within 14.0 seconds.
Failure Log FL-27D — Hallucinated Policy Citations in Early LLM-Generated Auditor Narratives (v3.1)
-
Incident Description: When generating prose control implementation descriptions for ISO 27001 Annex A, an early prompt allowed the LLM to reference a
"Quarterly Disaster Recovery Tabletop Exercise"that was written in the company’s policy PDF but had only actually been executed semi-annually in Jira evidence tickets. -
Root Cause Analysis: Synthesizing auditor narratives from written policy documents (
What we say we do) rather than verified execution artifacts (What the Merkle ledger proves we did) creates dangerous audit misrepresentations. -
Architectural Remediation: Enforced Evidence-First Narrative Grounding:
Auditor-Brief-Nodeis barred from claiming any operational cadence or control activity unless linked to a verifiedmerkle_leaf_sha256execution record; if policy text statesQuarterlybut verified evidence showsSemi-Annual (180d), the engine explicitly flags a Policy-vs-Practice Cadence Variance to internal GRC leads 60 days before the external audit begins.
6. Protocol Execution Specification: Deterministic State Machine, Schemas & Production Telemetry (cmp-27 v3.5)
To enable enterprise engineering and compliance teams to audit and replicate cmp-27 v3.5 in production, this section documents the Deterministic Finite State Machine (FALCONIC-DASG-CS27), the Canonical Production Execution Payload, the Disaggregated Production Cohort Telemetry Matrix, and our Pre-Deployment Engineering Readiness Checklist.
6.1 Deterministic State Transition Matrix (FALCONIC-DASG-CS27)
Every invocation of cmp-27 v3.5 is governed by a strict state machine enforcing precondition and postcondition invariants at each stage transition:
| State ID | State Name | Precondition Invariant | Active Node / Engine | Postcondition Verification Gate | Max Latency SLA | Fallback / Exception Transition |
|---|---|---|---|---|---|---|
S00_EVENT_HOOK |
Real-Time Cloud/IAM/Git/HR State Mutation Ingest | EventBridge, K8s Audit, Okta or Git PR event | Evidence-Collector-Swarm |
Canonical resource JSON normalized within 2.0s |
2.0s | S00_HOURLY_RECONCILE_POLL |
S01_INVARIANT_EVAL |
84 Canonical Invariant & Compensating Graph Check | Resource state + compensating subgraph | Control-Graph-Node |
Boolean invariant evaluated across all 5 frameworks | 3.1s | S04_DRIFT_REMEDIATION_PR |
S02_MERKLE_SIGN |
RFC 8785 Canonical Hash & RFC 3161 Timestamp | Verified evidence packet | Crypto-Ledger-Node |
SHA-256 leaf committed to WORM S3 + TSA signature | 1.4s | S02_SECONDARY_TSA_PROVIDER |
S03_NARRATIVE_SYN |
Merkle-Anchored Auditor Narrative & Matrix Update | Signed leaf hash + framework ontology | Auditor-Brief-Node |
100% of claims bound to merkle_leaf_sha256 |
4.2s | S03_TEMPLATE_ONLY_EMIT |
S04_DRIFT_REMEDIATION |
Autonomous Terraform / IAM Remediation PR | Invariant violation detected (Pass == 0) |
Terraform-Remediation-Node |
terraform plan passes syntax & blast-radius check |
3.3s | S98_SECOPS_PAGERDUTY_ALERT |
S05_AUDITOR_EXPORT |
One-Click Big-4 Cross-Framework Audit Package | Audit window query [t_start, t_end] |
Package-Compiler-Node |
ZIP with Merkle verifier script, populations & samples | 8.5s | S98_GRC_LEAD_REVIEW |
6.2 Canonical Production Execution & Verification Payload (cmp-27 v3.5)
Below is an anonymized production telemetry and verification payload emitted by cmp-27 v3.5 during live operation within the Continuous Multi-Framework Regulatory Compliance & Cryptographic GRC Auditing enclave:
{
  "protocol_version": "FALCONIC-CMP-27-V3.5",
  "audit_event_id": "grc_evt_20261018_0049182",
  "detection_latency_seconds": 13.8,
  "canonical_invariant_id": "INV_019_DATA_IN_TRANSIT_ENCRYPTION_STRICT",
  "satisfied_regulatory_controls": [
    "SOC2_CC6.7_TRANSMISSION_PROTECTION",
    "ISO_27001_2022_A.8.24_USE_OF_CRYPTOGRAPHY",
    "HIPAA_164.312_e_1_TRANSMISSION_security",
    "PCI_DSS_V4_REQ_4.2.1_STRONG_CRYPTOGRAPHY",
    "GDPR_ART_32_1_A_PSEUDONYMIZATION_AND_ENCRYPTION"
  ],
  "evaluated_resource": {
    "asset_arn": "arn:aws:eks:us-east-1:112233445566:pod/prod-claims-processor-7f9b8c",
    "primary_control_native_tls": false,
    "compensating_control_subgraph_satisfied": true,
    "compensating_proofs": [
      {"control": "ENVOY_SIDECAR_ISTIO_MTLS_STRICT", "spiffe_verified": true},
      {"control": "CILIUM_NETPOL_BLOCK_DIRECT_UNENCRYPTED_POD_IP", "policy_sha256": "8a91b20c..."}
    ]
  },
  "cryptographic_provenance": {
    "merkle_tree_date": "2026-10-18",
    "merkle_leaf_sha256": "9f86d081884c7d659a2feaa0c55ad015a3bf4f1b2b0b822cd15d6c15b0f00a08",
    "rfc3161_tsa_serial": "TSA_DIGICERT_2026_994820114",
    "worm_s3_object_lock_mode": "COMPLIANCE_RETENTION_7_YEARS"
  }
}
6.3 Disaggregated Production Telemetry Matrix Across Operational Cohorts
The table below disaggregates verified production performance for cmp-27 v3.5 across key operational cohorts and workload tiers, benchmarked against legacy baselines as documented in FalconicLab Case Studies:
| Regulatory Framework & Control Domain | Mapped Controls (n=312) |
Shared Canonical Invariants | Manual Prep Hours / Yr | FalconicLab cmp-27 Hours / Yr |
Evidence Mapping Precision | Drift Detection Latency | External Audit Exceptions |
|---|---|---|---|---|---|---|---|
| SOC2 Type II (Security, Availability, Confidentiality) | 94 controls | 68 invariants | 1,120 hrs | 140 hrs (-87.5%) | 99.5% | 13.4s | 0 exceptions |
| ISO/IEC 27001:2022 (ISMS & Annex A Controls) | 93 controls | 74 invariants (89% overlap) | 980 hrs | 118 hrs (-88.0%) | 99.4% | 14.1s | 0 non-conformities |
| HIPAA Security & Privacy Rule (§164.308–316) | 48 controls | 41 invariants (92% overlap) | 640 hrs | 82 hrs (-87.2%) | 99.2% | 13.9s | 0 findings |
| PCI-DSS v4.0 (Cardholder Data Environment) | 52 controls | 46 invariants (85% overlap) | 590 hrs | 78 hrs (-86.8%) | 99.1% | 14.6s | 0 ROC exceptions |
| GDPR Technical & Organizational Measures (Art. 25/32) | 25 controls | 22 invariants (95% overlap) | 310 hrs | 40 hrs (-87.1%) | 99.3% | 14.2s | 0 DPA audit gaps |
| Total / Cross-Framework Enterprise GRC Portfolio | 312 Controls | 84 Unique Invariants | 3,640 hrs / yr | 458 hrs / yr (-87.4%) | 99.3% Precision | 14.0s Median | 0.0 Audit Exceptions |
6.4 Deep-Dive Production Implementation: Autonomous Terraform Drift Remediation PRs & Policy-vs-Practice Gap Detection
When a developer or emergency maintenance script introduces a compliance regression in AWS, GCP, or Kubernetes (such as creating an unencrypted S3 bucket, opening security group 0.0.0.0/0 on port 22, or merging a repo without branch protection), alerting a dashboard is only half the battle.
Within 14.0 seconds of the CloudTrail or GitHub webhook event, Terraform-Remediation-Node:
-
Traces the Cloud Resource Back to its Originating IaC AST File: Queries OpenTofu/Terraform state lineage tags (
git_repo,tf_module_path,resource_address) to locate the exact.tffile and line number managing that resource (or generates animportblock if the resource was created via ClickOps in the AWS Console). -
Synthesizes & Sandboxes a Minimal Remediation Patch: Generates the exact HCL patch (e.g., attaching
aws_s3_bucket_server_side_encryption_configurationwith the production KMS key ARN), runsterraform validateandtflintinside an isolated container, and opens a GitHub Pull Request assigned to the offending commit author with the exact regulatory citation (violates SOC2 CC6.1 & ISO A.8.24)—shrinking Mean Time to Remediate compliance drift from 19 days to 14 minutes.
6.5 Pre-Deployment Engineering Readiness Checklist (cmp-27 v3.5)
Engineering leaders deploying cmp-27 v3.5 into production Continuous Multi-Framework Regulatory Compliance & Cryptographic GRC Auditing environments must enforce five mandatory architectural guardrails:
-
Map Overlapping Frameworks to Canonical Technical Invariants (
Collect Once, Satisfy Many): Never run separate evidence collectors for SOC2, ISO 27001, and HIPAA; map all 310+ clauses onto 84 canonical technical assertions. -
Encode Compensating Controls Explicitly as Boolean Subgraphs: Prevent false-positive alerts on service-mesh and zero-trust architectures by evaluating pod + sidecar + network policy configurations jointly.
-
Cryptographically Sign and RFC 3161 Timestamp Every Daily Evidence Snapshot: Eliminate Big-4 auditor skepticism over AI-generated reports by anchoring every raw JSON telemetry proof into a WORM S3 Merkle tree.
-
Audit Immutable Image Digests & Admission Gates for Ephemeral Containers: Do not sample short-lived pod IDs; capture SLSA build attestations and Kyverno/OPA admission logs to prove continuous compliance across auto-scaling clusters.
-
Verify Operational Practice Against Written Policy Cadence 60 Days Pre-Audit: Automatically cross-check every promise in corporate policy PDFs (
"Quarterly DR Test") against actual dated execution artifacts in Jira/Git.
7. Production Infrastructure, Hardware Topology & Chaos Engineering Benchmarks (cmp-27 v3.5)
7.1 High-Availability Cloud, Edge & Enclave Deployment Topology
To continuously audit 312 regulatory controls across 5 overlapping compliance frameworks (SOC2 Type II, ISO/IEC 27001:2022, HIPAA Security Rule, PCI-DSS v4.0, and GDPR Art. 25/32) across 14 AWS/GCP cloud accounts, 6 Kubernetes clusters, Okta, Rippling/Workday, and 280 GitHub repositories with a 14.0-second drift detection SLA, FalconicLab engineered an event-driven cryptographic GRC enclave:
- Serverless Go/Rust Event-Driven Harvester Swarm (
Evidence-Collector-Swarm):- Triggered in real time via AWS EventBridge / CloudTrail, GCP Audit Logs, Kubernetes Validating/Mutating Admission Webhooks (
Kyverno / OPA), Okta System Log Webhooks, and GitHub App PR Events. - Normalizes raw resource state mutations into RFC 8785 Canonical JSON within
2.0 secondsof any infrastructure or identity change.
- Triggered in real time via AWS EventBridge / CloudTrail, GCP Audit Logs, Kubernetes Validating/Mutating Admission Webhooks (
- Neo4j + Qdrant Bipartite Control Homomorphism Graph (
Control-Graph-Node):- Maps all 312 framework clauses onto 84 Canonical Technical Invariant Predicates evaluated via monotone Boolean compensating-control formulas (e.g., verifying
Native_Container_TLS == 1 OR (Istio_Envoy_mTLS_Strict == 1 AND Cilium_NetPol_Block_Plaintext == 1)), preventing false non-compliance alerts on cloud-native service meshes. - Maintains a live Cross-System Identity & Credential Lineage Graph linking every AWS IAM key, GitHub Personal Access Token, database role, and service principal back to its human creator’s HR employee ID.
- Maps all 312 framework clauses onto 84 Canonical Technical Invariant Predicates evaluated via monotone Boolean compensating-control formulas (e.g., verifying
- RFC 3161 Trusted Timestamp & WORM S3 Object-Lock Merkle Ledger (
Crypto-Ledger-Node):- Hashes every daily control evaluation and event proof into a SHA-256 Merkle Audit Tree, co-signs the daily root hash via an external DigiCert RFC 3161 Trusted Timestamp Authority (TSA), and commits the package to AWS S3 Object Lock (
COMPLIANCEmode, 7-year retention)—providing Big-4 external auditors with mathematical proof of contemporaneous evidence collection.
- Hashes every daily control evaluation and event proof into a SHA-256 Merkle Audit Tree, co-signs the daily root hash via an external DigiCert RFC 3161 Trusted Timestamp Authority (TSA), and commits the package to AWS S3 Object Lock (
- Sandboxed OpenTofu / Terraform Remediation PR Synthesizer (
Terraform-Remediation-Node):- Traces non-compliant cloud resources back to their exact
.tffile and line number via state lineage tags, runsterraform validate+tflintin an isolated container, and opens a ready-to-merge remediation Pull Request within 14.0 seconds.
- Traces non-compliant cloud resources back to their exact
7.2 Chaos Engineering & Adversarial Fault-Injection Drills
Before certifying cmp-27 v3.5 as STATUS: NOMINAL in the FalconicLab Live Experiments & Systems Registry, our reliability and security engineering teams subjected the production deployment to three destructive fault-injection and adversarial chaos drills:
- Chaos Drill
CD-27A— Unannounced “ClickOps” Security Group & Unencrypted S3 Bucket Drift Injection: Red-team engineers manually logged into the AWS Console (ClickOps) and created an S3 bucket without KMS encryption while opening port22 (SSH)to0.0.0.0/0on a staging EKS worker security group.Evidence-Collector-Swarmintercepted the CloudTrail event via EventBridge in1.8s,Control-Graph-Nodeflagged the simultaneous violation ofSOC2 CC6.1,ISO A.8.24,HIPAA §164.312(a)(2)(iv), andPCI-DSS 1.3.1in3.1s, andTerraform-Remediation-Nodeopened a validated Terraform import + remediation PR and alerted SecOps in 13.6 seconds total. - Chaos Drill
CD-27B— Offboarded Contractor “Orphaned GitHub PAT & Snowflake Key” Deprovisioning Audit: Simulated the immediate HR termination of a senior data contractor in Workday/Okta while leaving a personal GitHub deploy token and a secondary Snowflake RSA key active under a team service account created by that contractor 4 months earlier. While standard GRC tools markedEmployee Offboarding = PASSbased solely on Okta SSO deactivation,Control-Graph-Node’s Identity Lineage Graph traced both orphaned keys to the contractor’s creator ID in4.2 secondsand automatically revoked them via GitHub/Snowflake admin APIs. - Chaos Drill
CD-27C— Big-4 External Auditor 365-Day Merkle Verification & Ephemeral Pod Sampling: External SOC2 Type II auditors selected 60 random timestamps across the 12-month audit window and tested the cryptographic Merkle inclusion proofs and SLSA container image attestations using an independent open-source Python verifier script. 60 out of 60 (100.0%) proofs verified with zero tampering, zero missing ephemeral pod populations, and 0.0 audit exceptions.
7.3 Executive Total Cost of Ownership (TCO) & 12-Month Financial ROI Ledger
Deploying cmp-27 v3.5 across all 5 regulatory frameworks (SOC2 Type II, ISO 27001, HIPAA, PCI-DSS v4.0, GDPR) delivered over $840,000 in verified annual engineering, GRC, and sales-velocity value:
- Engineering & GRC Audit Preparation Labor Reclaimed (
-87.4%Reduction):- Slashed annual manual screenshot collection, CSV population exports, and narrative writing from
3,640 hours/yeardown to 458 hours/year, reclaiming 3,182 senior DevOps, SecOps, and GRC engineering hours ($493,000/year).
- Slashed annual manual screenshot collection, CSV population exports, and narrative writing from
- External Auditor & SaaS GRC Consolidation Savings:
- Retired two overlapping legacy GRC checklist subscriptions (
$95,000/year) and reduced external Big-4 audit billable fieldwork hours by28%($62,000/year) thanks to one-click cryptographic Merkle evidence packages.
- Retired two overlapping legacy GRC checklist subscriptions (
- Enterprise Sales Security-Questionnaire Acceleration:
- Automated generation of Merkle-backed security questionnaire responses shortened enterprise deal legal/security review cycles by 11.4 days, accelerating $190,000+/year in time-value of ARR.
- Total Daily Control Audit & Compute Cost: $0.08 per control-day (
$9,110/yearacross 312 controls)—a 92x net financial return.